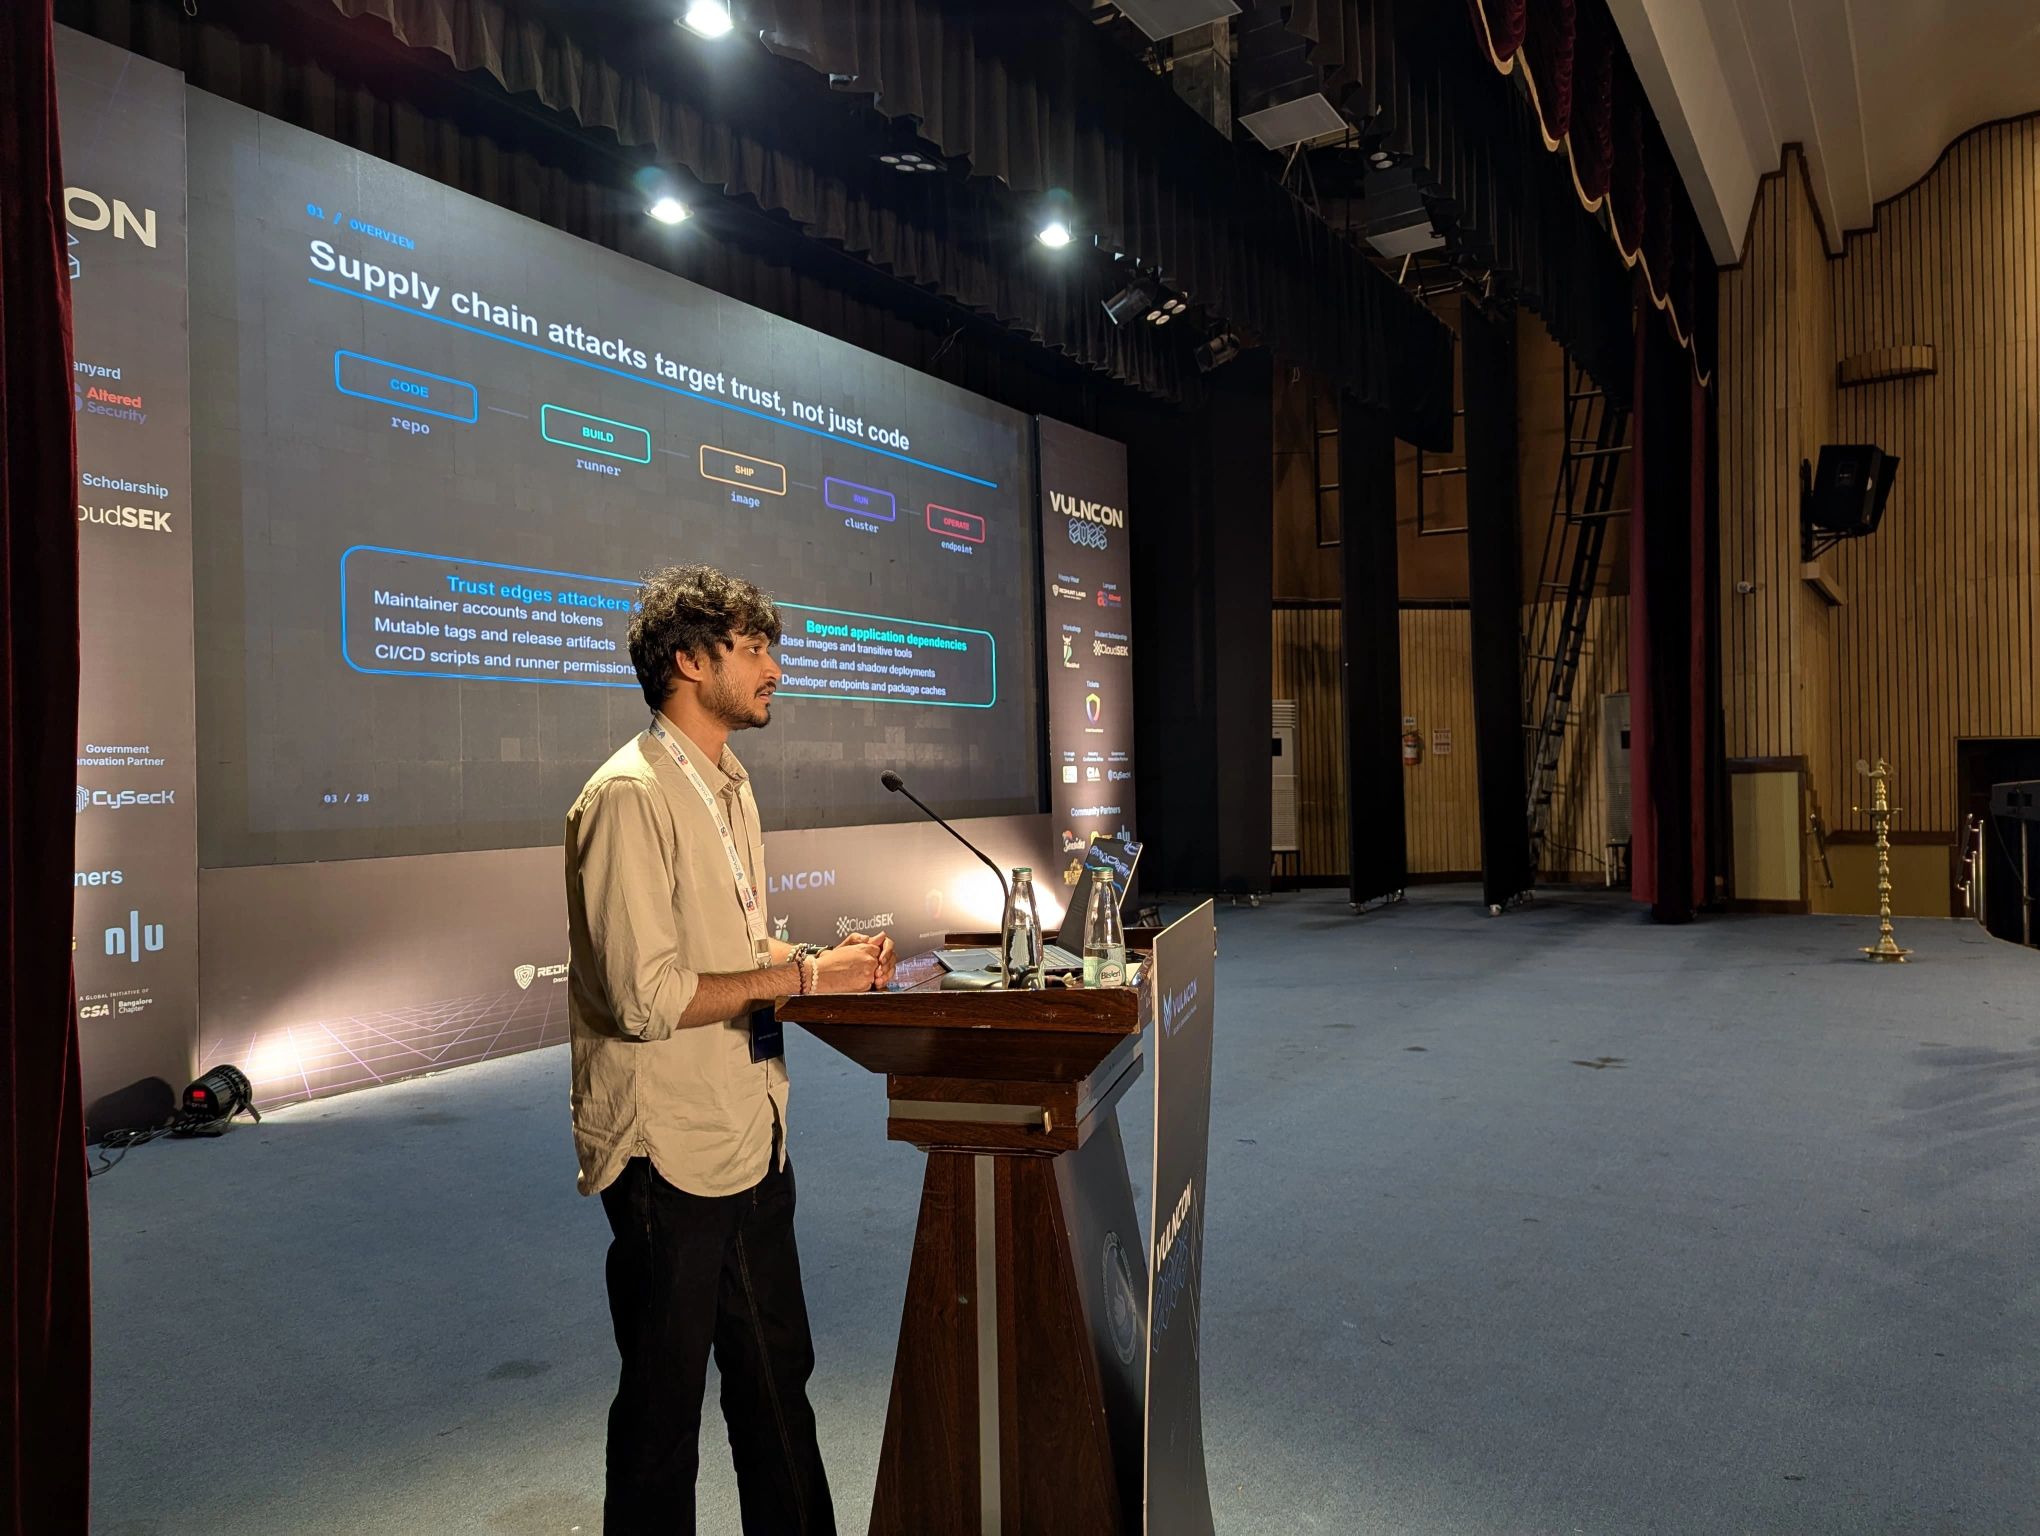
Conference
VulnCon 2026
June 12, 2026
Abstract
The software supply chain security landscape operates on a dangerous assumption — that Software Composition Analysis (SCA) tools, by parsing lockfiles like package-lock.json, go.sum, or requirements.txt, produce a complete and accurate Software Bill of Materials. They don’t. Lockfiles are a point-in-time artifact of declared intent, not a reflection of what’s actually executing in your build pipelines, container images, or production clusters. There is a big gap when it comes to workflows like GitHub Actions. The gap between the two is where real supply chain attacks live — and where current tooling is blind. This is how a lot of companies were affected by Shai-Hulud.
This research systematically maps and exploits three distinct dependency ingestion vectors that fall entirely outside the lockfile model, producing what we term Phantom Dependencies — components that are fetched, executed, and trusted by your infrastructure but are invisible to every major SCA scanner on the market.
Publication
Related Project
🔗 SupplyDrift — Discover hidden dependencies across repositories, container images, cloud runtimes, and endpoints.